Arrives unannounced
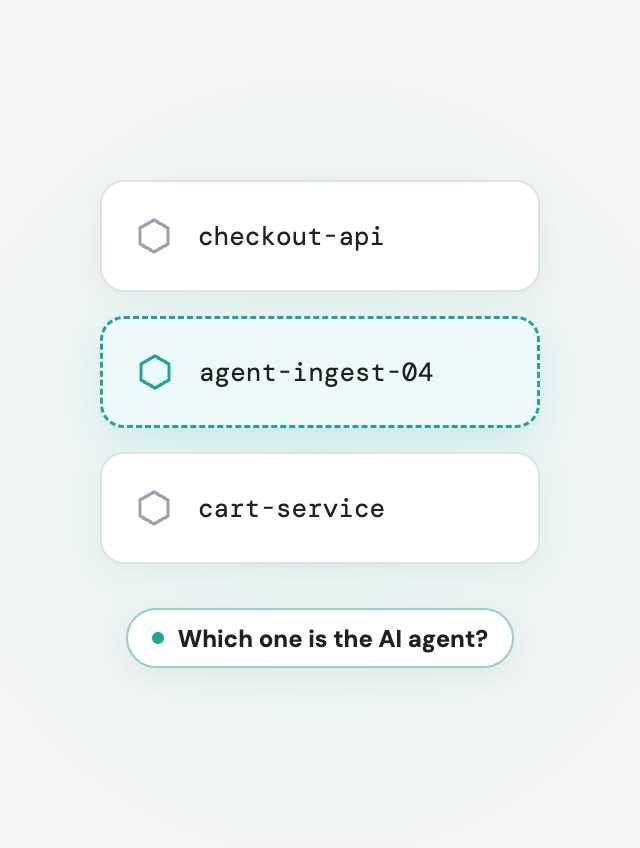
A tenant deploys one like any other pod. Nothing marks it as one.
Lynx by Tigera | AI agent security on Kubernetes
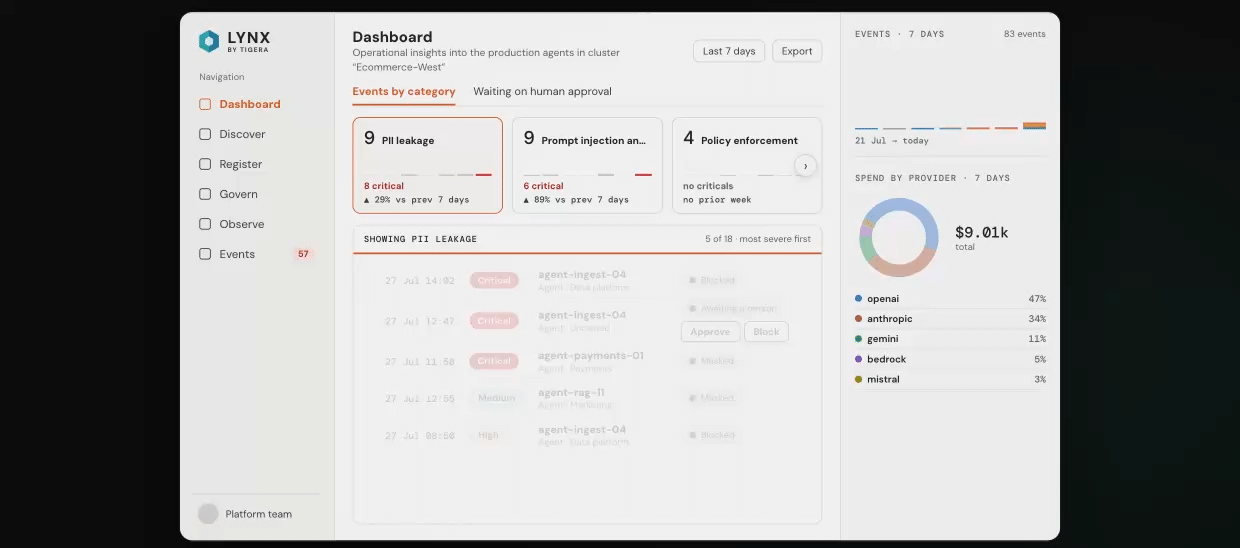
Lynx finds the AI agents running in your Kubernetes clusters, checks every call they make, and contains agents that step out of line without any code changes.
From the team behind Project Calico, securing 8M+ Kubernetes nodes and 1M+ clusters every day.
Tigera secures Kubernetes for the world's most demanding enterprises






AI agent: the new workload
A decade of platform engineering made Kubernetes safe for microservices: workload identity, network policy, mTLS, default-deny. But AI agents don’t behave like the workloads your stack was built for.
A tenant deploys one like any other pod. Nothing marks it as one.
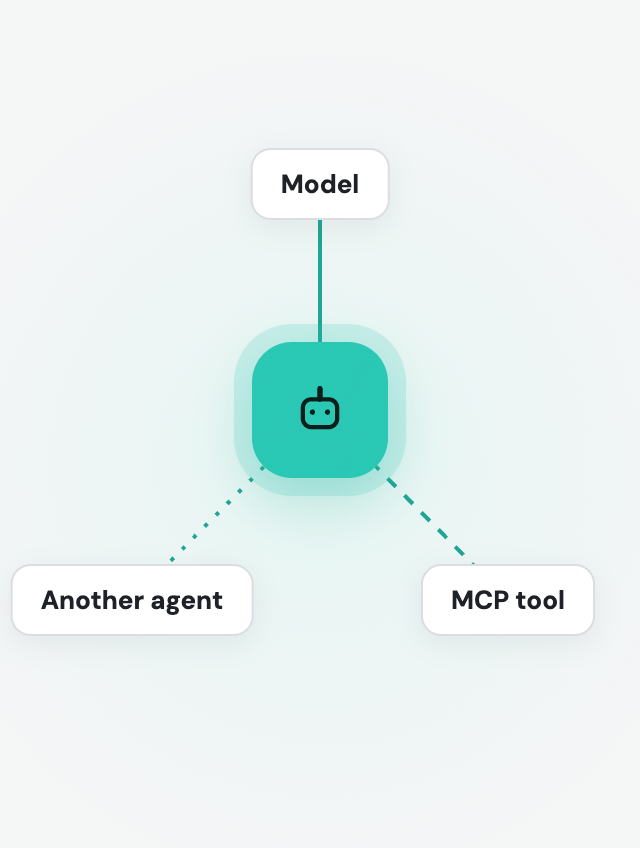
Every run can call a different model, MCP tool or other agent, on behalf of a different user.
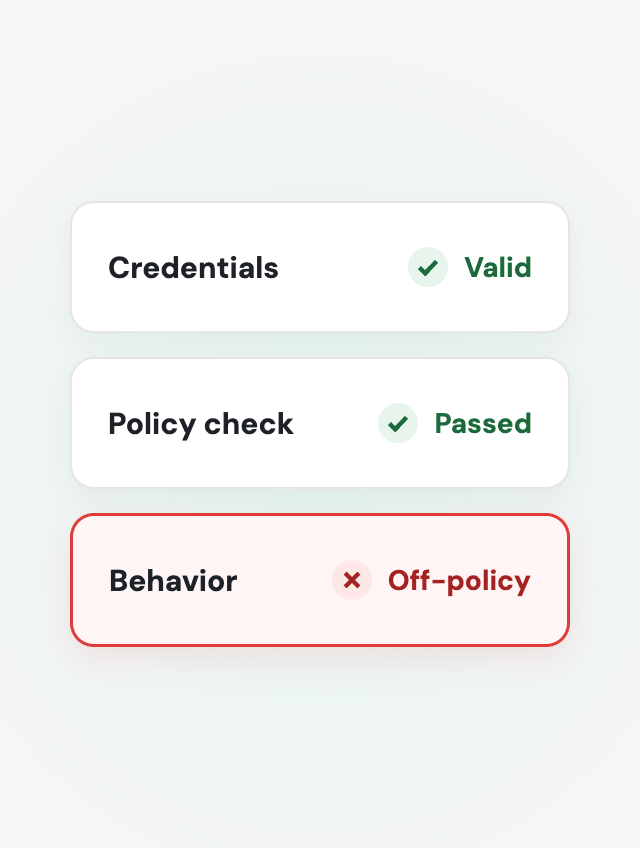
Passing every policy check is not the same as behaving.
Do you know how many AI agents are running on your cluster right now?
Get startedOne gap, three teams
Tenants are deploying AI agents you never approved. You find out when something breaks, or when someone asks how many there are.
Your agent is ready to ship but stuck in a security review. To get approved, it often has to give up the access that made it useful.
You're asked to approve AI agents you can't defend in an audit. Saying no stalls the business but saying yes without a record is worse.
One gap sits under all three: no single place says what each agent is,
what it is allowed to do, and what it actually did.
Our point of view
Not beside it. Not around it.
Not left to each team to secure alone.
On Kubernetes: identified, governed and contained like every other production workload. Platform teams offer AI agents to every team on day one. AI teams ship with the access they need. Security has an answer when someone asks what happened.
Lynx delivers this.
How Tigera Lynx works
01 SEE
Lynx watches from the kernel on every node and finds the AI agents running across your clusters, including the ones nobody told you about. Each one lands in a central registry with an owner, a purpose and a decision: register it, or quarantine it.
02 GOVERN
Every call an agent makes to a model, an MCP tool or another agent passes one checkpoint. It goes through only if policy says this agent may make this call, for this user, right now. Identity comes from the source you already trust, and long-lived API keys give way to short-lived, scoped tokens at every hop.
03 CONTAIN
When an agent goes around the checkpoint, or behaves badly on a valid credential, Lynx catches it in the kernel and quarantines that one agent mid-run. Its tenant keeps running. So does everyone else's.
04 PROVE
For every call, Lynx records which agent made it, for whom, what it touched and which policy allowed it. Audit logs flow into the tools your teams already use, so an audit request means running a report, not digging through logs.
Built for the team you're on
Platform engineering
Offer AI agents to every team on day one, with identity, policy and containment built in. One install, any CNI, and no build project stitching together gateways, policy engines and eBPF tooling.
Learn more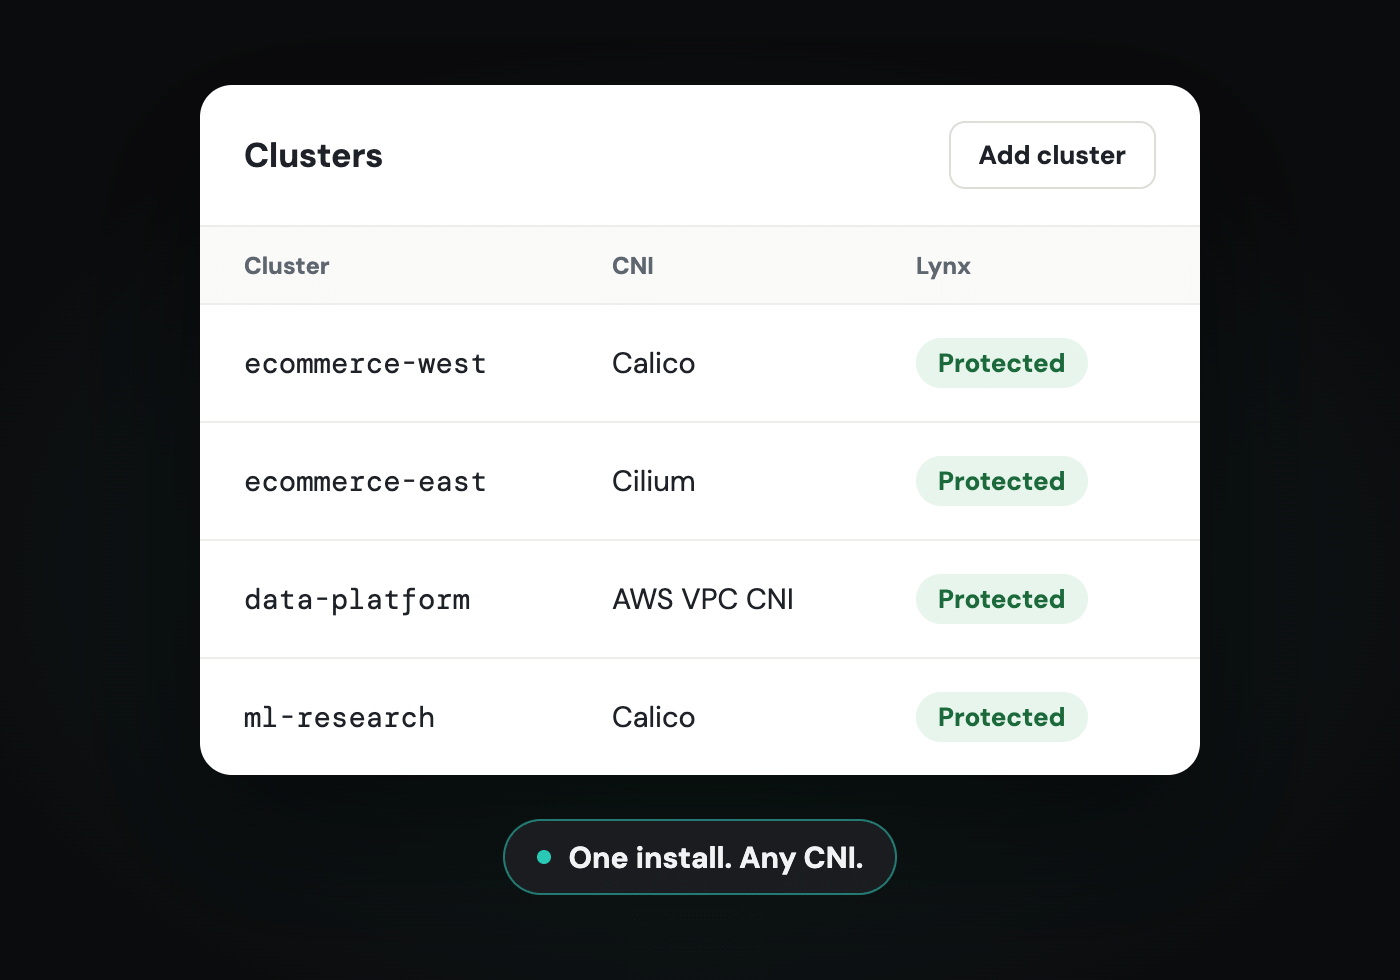
AI teams
Security can approve real access because any agent can be contained mid-run. No SDK, nothing to rewrite, and a new agent ships within limits everyone already agreed on.
Watch the 3-minute demo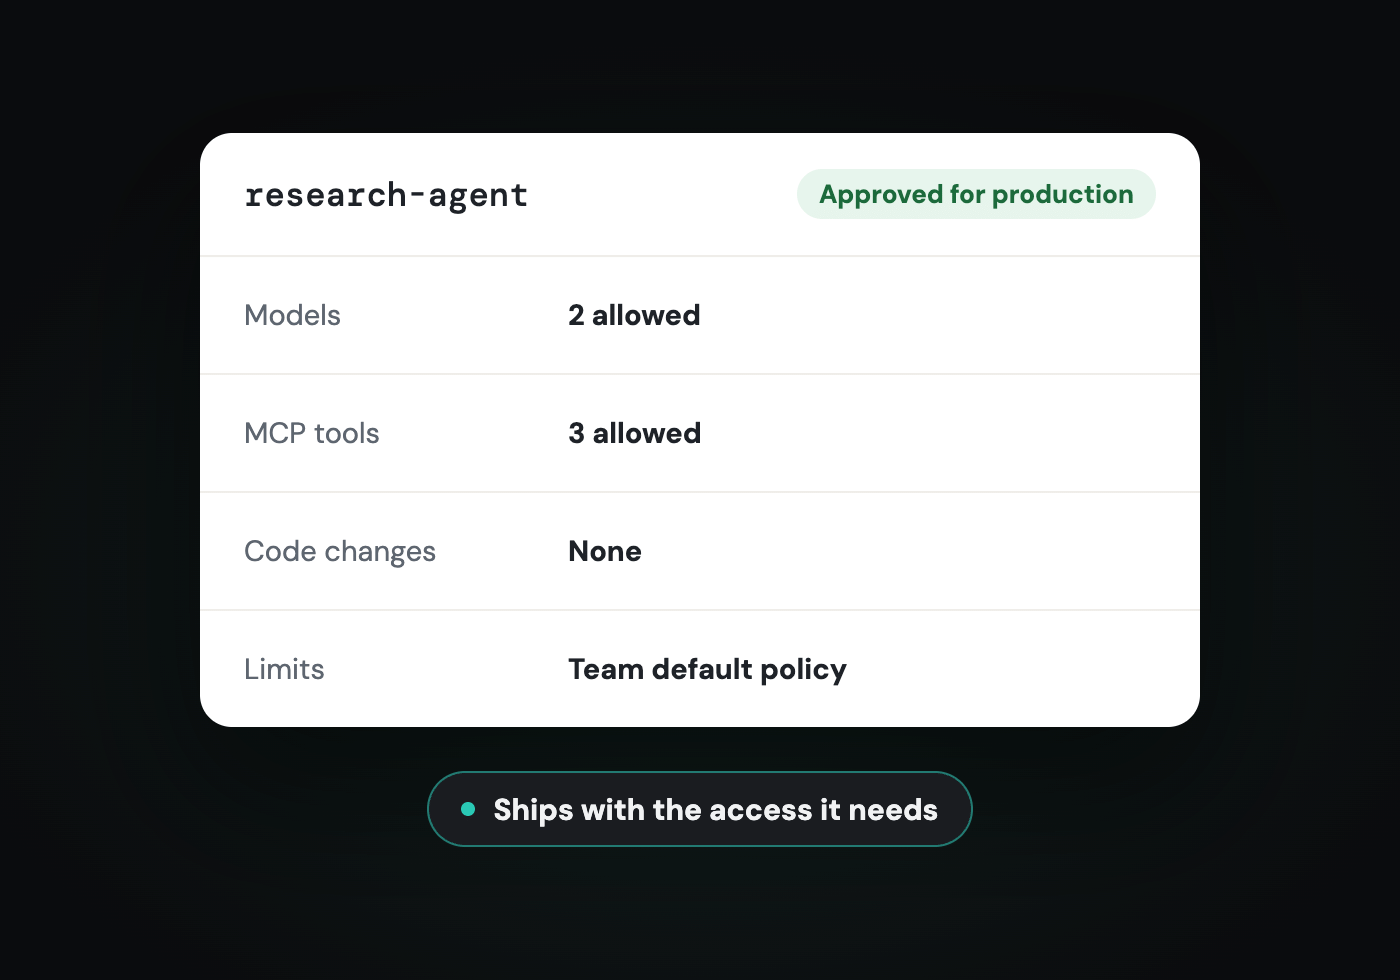
Security teams
Enforcement inside Kubernetes, in your own clusters, feeding the AI security program you already run. Every agent call comes with who made it, for whom, and why it was allowed.
Learn more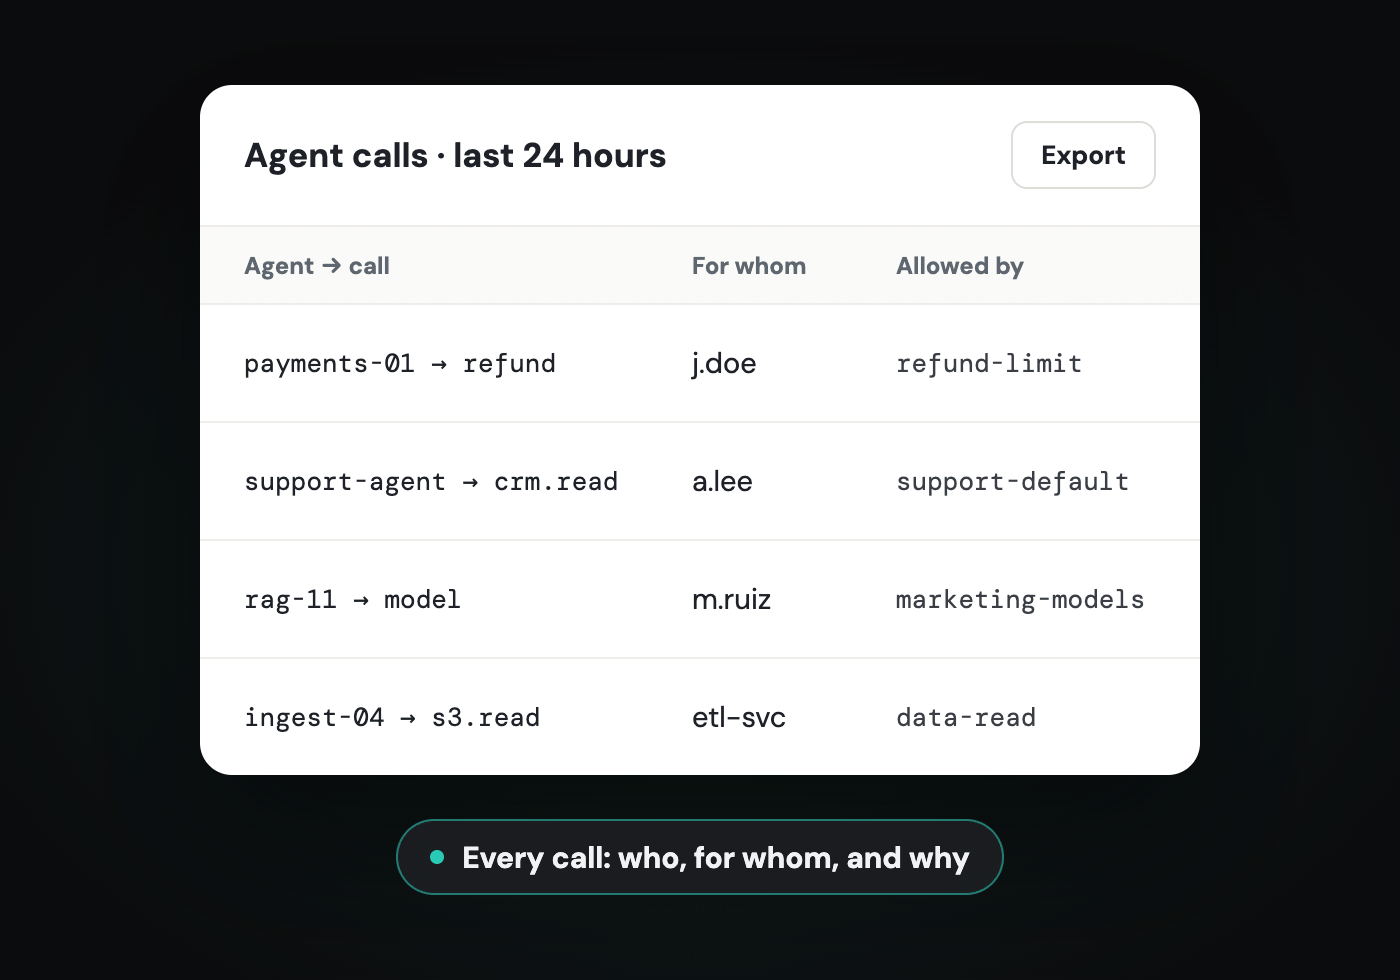
Trusted in production
The teams that trust Tigera to secure Kubernetes at scale.
Our relationship with Tigera feels like more than just a company selling us a product. They have been a true partner, helping us solve problems and providing valuable insights.
The support Tigera’s team provided on the calls was great—it was levels above what we have received in the past from other security solution providers with our previous tools.
The support from Tigera has been absolutely phenomenal. They have been unbelievably helpful, even in situations where the issue wasn’t related to the product itself.
Tigera’s support team has been excellent—their on-call engineers worked with me after hours and solved issues on the spot.

Start with the number
One install shows which teams are running AI agents and what each one calls. Everything else follows from that number.